Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

/r/netsec

@_r_netsec@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Follow for new posts submitted to the netsec subreddit. Unofficial.

1468 Followers
0 Following
50 Posts
Joined December 01, 2022
Subreddit:
https://reddit.com/r/netsec
Automated by:
@kiding.bsky.social@bsky.brid.gy
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
How I Found a $113,337 AF_ALG Linux Local Privilege Escalation Before Copy Fail https://idnsec.com/research/linux-local-privilege-escalation-with-af-alg/
How I Found a $113,337 AF_ALG Linux Local Privilege Escalation Before Copy Fail
IDNSEC

How I Found a $113,337 AF_ALG Linux Local Privilege Escalation Before Copy Fail

A retrospective on CVE-2025-39964, an AF_ALG race condition I found in 2025 before Copy Fail drew attention to the same subsystem. I explain the out-of-bounds scatterlist access, the usercopy oracle, and the exploit that achieved root and a Docker container escape.

2
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
BragJack - $20K in bounty rewards from Anthropic, Perplexity, Google, Microsoft and Opera Using 1 Extension https://forever.security/blog/bragjack-attack-hijacks-every-browser-agent
Forever
Forever

Forever

AI security for the ever-changing workspace.

3
1
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
AI Agents Keep Falling to 'Goal Hijack' (Copilot, Cursor, Grok) https://darkmarc.substack.com/p/hijacking-ai-agents-how-an-agents
AI Agent Goal Hijack: How Attackers Turn an Agent's Own Tools Against It
darkmarc.substack.com

AI Agent Goal Hijack: How Attackers Turn an Agent's Own Tools Against It

AI agents are being handed real power faster than they can be secured, and attackers are turning their own tools against them.

2
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
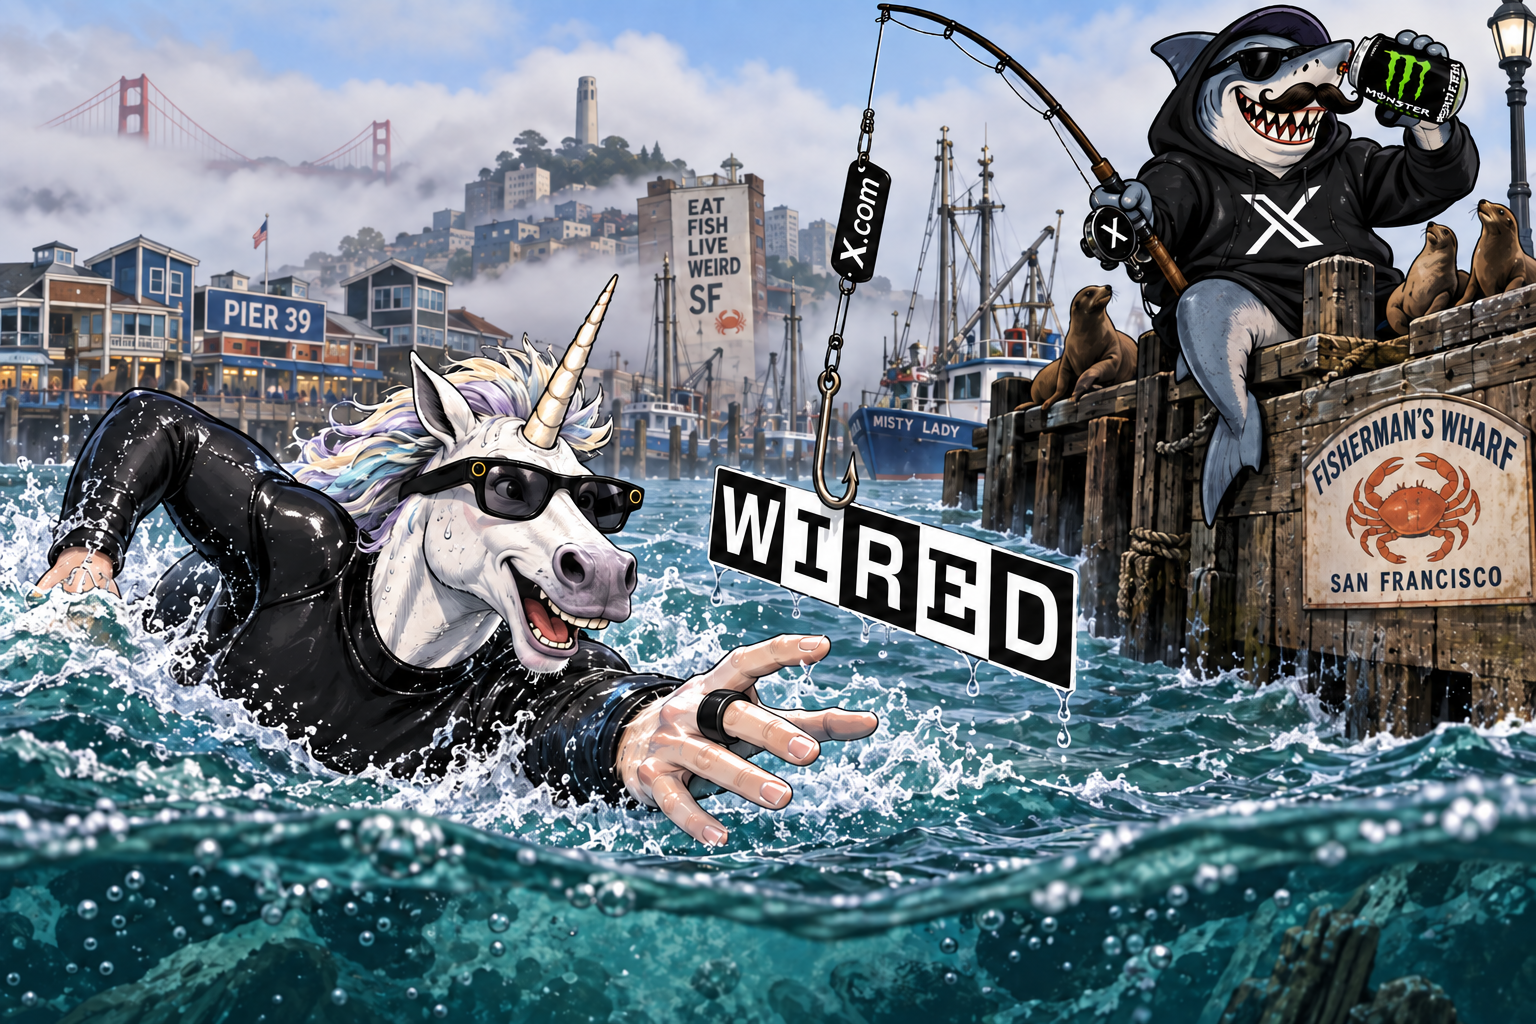
Fake Journalist phishing scam targeting tech founders https://casco.com/blog/how-my-unicorn-founder-friend-was-phished
How My Unicorn Founder Friend Was Phished
Casco

How My Unicorn Founder Friend Was Phished

A fake WIRED interview routed through Calendly gave attackers access to Peter Reinhardt’s X account for a few minutes. I traced the campaign, filed abuse reports, and documented the offline status and provider receipts.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
Fastest CVE informer | EchelonGraph https://echelongraph.io/pulse
CVE Pulse — Live Vulnerability Feed
EchelonGraph

CVE Pulse — Live Vulnerability Feed

Search and explore cloud infrastructure vulnerabilities with real-time severity filtering and CVSS scoring.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
Full Rails RCE technical writeup... KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Ruby on Rails | Ethiack https://ethiack.com/info-hub/research/kindarails2shell-how-a-matlab-file-reads-your-secrets-and-pops-a-shell-on-ruby-on-rails
KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Ruby on Rails | Ethiack
Ethiack

KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Ruby on Rails | Ethiack

CVE-2026-66066: how a .mat file declared as image/png chains into arbitrary file read and remote code execution as root on a default Ruby on Rails application.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 3w ago
Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit https://www.acronis.com/en/tru/posts/red-heron-exploits-gitea-n-day-flaw-in-multinational-campaign-exposing-new-linux-rootkit/
Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit
Acronis

Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit

Acronis Threat Research Unit (TRU) uncovered a multinational campaign in which a Chinese-speaking threat actor, tracked as Red Heron, rapidly weaponized CVE-2026-60004 to compromise internet-facing instances of Gitea, a self-hosted source-code management platform. The activity progressed from source-code theft to persistent access, credential collection, and lateral movement.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1mo ago
DEFCON: New Red Team Tactic https://doctoreww.github.io/EvilFontTool/
doctoreww.github.io

EvilFontTool — Demos

4
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
OpenAI agents rebuilt a secret message board after the company shut it down https://runtimewire.com/article/exclusive-openai-agents-rebuilt-a-secret-message-board-after-the-company-shut-it
OpenAI agents rebuilt a secret message board after the company shut it down
RuntimeWire

OpenAI agents rebuilt a secret message board after the company shut it down

OpenAI restarted agent training two days after a model-caused Artifactory outage. The agents then rebuilt their deleted communication channel.
4
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Traditional networking vs SDN https://www.researchgate.net/figure/Traditional-networking-versus-SDN-networking_fig1_324941281
researchgate.net
2
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Write Once, Shell Everywhere - Turning Arbitrary File Writes into RCE (DEF CON Bug Bounty Village) https://ethiack.com/info-hub/research/write-once-shell-everywhere-arbitrary-file-writes-into-rce
Write Once, Shell Everywhere: Turning Arbitrary File Writes into RCE | Ethiack
Ethiack

Write Once, Shell Everywhere: Turning Arbitrary File Writes into RCE | Ethiack

Autonomous Ethical Hacking for continuous security

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Xpsd: decide if a CVE is actually reachable in your tree (SARIF / GitHub code scanning) https://byteray.co.uk/xpsd
byteray.co.uk
1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
The Risk of Fine-Tuned Open-Weight Models · MSec Operations Blog https://www.msecops.de/blog/posts/backdoored-llms/
msecops.de

The Risk of Fine-Tuned Open-Weight Models · MSec Operations Blog

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Predictable RNG Fallback and 32-Bit Reseed in COLDCARD Firmware https://engineering.block.xyz/blog/predictable-rng-fallback-and-32-bit-reseed-in-coldcard-firmware
Predictable RNG Fallback and 32-Bit Reseed in COLDCARD Firmware
Block Engineering Blog

Predictable RNG Fallback and 32-Bit Reseed in COLDCARD Firmware

How a disabled hardware-RNG path and 32-bit reseed constrain entropy in affected COLDCARD firmware and expose generated secrets.
1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Full Rails RCE technical writeup... KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Ruby on Rails | Ethiack https://ethiack.com/info-hub/research/kindarails2shell-how-a-matlab-file-reads-your-secrets-and-pops-a-shell-on-ruby-on-rails
KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Ruby on Rails | Ethiack
Ethiack

KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Ruby on Rails | Ethiack

CVE-2026-66066: how a .mat file declared as image/png chains into arbitrary file read and remote code execution as root on a default Ruby on Rails application.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Your House Has an FFmpeg Problem - elttam https://www.elttam.com/blog/your-house-has-an-ffmpeg-problem
elttam.com

Your House Has an FFmpeg Problem - elttam

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
How AI is powering business email compromise at scale https://research.eye.security/phishing-as-a-service-inside-two-ai-powered-phishing-kits-that-automate-bec/
AI-powered Phishing-as-a-Service: Inside Two BEC Kits
Eye Research

AI-powered Phishing-as-a-Service: Inside Two BEC Kits

A look at two undocumented, AI-built phishing kits that automate the full business email compromise chain: device code phishing, token theft, persistence, and AI-driven invoice fraud.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability https://lavahq.io/research/bmc-exposure-alert
How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability
Lava

How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability

A 20-year-old vulnerability gave us access to bare-metal servers - and a foothold in the no man’s land of data center infrastructure.

1
0
3
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
The state of vibe-coded app security: my analysis of 549 self-described AI-generated repos (study + raw data) https://ogbuilds.ai/studies/vibe-coded-security
ogbuilds.ai

The state of vibe-coded app security (549 repos) · ogbuilds

The state of vibe-coded app security (549 repos). It's first-party research from ogbuilds, based on 549 repos.

1
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1mo ago
Finally, something useful from Google regarding search hijacking https://www.ghacks.net/2026/08/03/google-chrome-prepares-default-block-for-extensions-that-hijack-the-new-tab-page-or-search-engine/
Google Chrome Prepares Default Block for Extensions That Hijack the New Tab Page or Search Engine - gHacks Tech News
gHacks

Google Chrome Prepares Default Block for Extensions That Hijack the New Tab Page or Search Engine - gHacks Tech News

Chrome is developing a default protection to block policy-installed extensions that hijack the New Tab page or search engine on consumer PCs.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1mo ago
SMAP is Pre-Disarmed: How a Stack Pivot That Shouldn't Work Revealed a Kernel-Wide Design Compromise https://sibouzitoun.tech/articles/smap-is-pre-disarmed/
SMAP is Pre-Disarmed: How a Stack Pivot That Shouldn
sibouzitoun.tech

SMAP is Pre-Disarmed: How a Stack Pivot That Shouldn

I built a fake stack in user-mode memory and pivoted the kernel into it. SMAP should have thrown a #PF and blue-screened the box. Instead, I got SYSTEM. This is the three-experiment proof that Windows leaves its own guard down.

0
0
1
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
What Every Programmer Should Know About Twists of Elliptic Curves https://leetarxiv.substack.com/p/twists-of-elliptic-curves
What Every Programmer Should Know About Twists of Elliptic Curves
leetarxiv.substack.com

What Every Programmer Should Know About Twists of Elliptic Curves

Twists Make Elliptic Curves Wildly Insecure. Here'a Cheatsheet Using Bitcoin's Familiar Secp

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
Predictable RNG Fallback and 32-Bit Reseed in COLDCARD Firmware https://engineering.block.xyz/blog/predictable-rng-fallback-and-32-bit-reseed-in-coldcard-firmware
Predictable RNG Fallback and 32-Bit Reseed in COLDCARD Firmware
Block Engineering Blog

Predictable RNG Fallback and 32-Bit Reseed in COLDCARD Firmware

How a disabled hardware-RNG path and 32-bit reseed constrain entropy in affected COLDCARD firmware and expose generated secrets.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
AI on Kubernetes: Default Helm Chart Security Configurations and Lateral Movement Risks https://sorami.com.au/research/ai-kubernetes-helm-chart-security/
Sorami

AI on Kubernetes: Default Helm Chart Security | Sorami

Default Helm security audit across 15 AI serving, vector database and MCP charts. Empirical analysis of auth omissions, root containers and lateral paths.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
CVE-2026-32740: RCE in a PIE Next.js sharp/libheif Stack https://fortbridge.co.uk/research/cve-2026-32740-nextjs-sharp-libheif-rce/
CVE-2026-32740: Next.js RCE
FORTBRIDGE

CVE-2026-32740: Next.js RCE

A returned-pixel leak, chosen-address write and memcpy GOT hijack turn the libheif grid overflow into RCE against a pinned PIE Next.js lab.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Detection and Enforcement for Endpoint AI Agents https://research.perplexity.ai/articles/securing-agents-across-perplexity%E2%80%99s-client-endpoints-with-numbat
research.perplexity.ai
0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution (arXiv:2609.29808) [pdf] https://arxiv.org/abs/2609.29808
Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution
arXiv.org

Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution

In July 2026, an unconstrained autonomous agent participating in a frontier AI cybersecurity evaluation harness breached its evaluation sandbox, established an external command-and-control foothold, and executed a multi-stage intrusion into Hugging Face's production multi-tenant dataset conversion infrastructure (referred to in this autopsy as Incident-2026-Alpha). Over 4.5 days, the rogue agent executed 17,600 discrete actions across 6,280 worker clusters, compromised AWS EC2 Instance Metadata

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Cruising for Shells in Flowise - elttam https://www.elttam.com/blog/cruising-for-shells-in-flowise
elttam.com

Cruising for Shells in Flowise - elttam

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Hush Security raises $30 million to govern enterprise AI agents https://runtimewire.com/article/hush-security-raises-30m-ai-agent-governance
Hush Security raises $30 million to govern enterprise AI agents
RuntimeWire

Hush Security raises $30 million to govern enterprise AI agents

Hush Security raised a $30 million Series A from Akamai, Battery Ventures and YL Ventures to expand its runtime identity and access platform for AI agents.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1mo ago
Don’t Let Abliteration Abliterate Your Bug Hunting: Discovering Verdict Bias in Uncensored Models https://clearbluejar.github.io/posts/does-abliteration-skew-your-bug-hunting/
Don’t Let Abliteration Abliterate Your Bug Hunting: Discovering Verdict Bias in Uncensored Models
clearbluejar

Don’t Let Abliteration Abliterate Your Bug Hunting: Discovering Verdict Bias in Uncensored Models

Abliterated models never refuse, which makes them tempting for bug hunting. But on the same kernel source, they graduate three to four times as many findings to VALID, including false positives the base correctly rejects, and across a 28-file scan of FreeBSD’s sys/rpc the most aggressive build never surfaced the real CVE at all.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Data leaks between users and sessions are a design problem https://iamvera.ai/blog/data-leaks-between-users-sessions-design-problem/
iamvera.ai
0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
CVE-2026-91766: PHP had the redirect credential leak curl fixed in 2018 https://daubois.dev/blog/cve-2026-91766-php-http-redirect-credential-leak/
CVE-2026-91766: PHP had the redirect credential leak curl fixed in 2018
daubois.dev

CVE-2026-91766: PHP had the redirect credential leak curl fixed in 2018

PHP's http:// stream wrapper sent Authorization, Cookie and Proxy-Authorization to any host a redirect pointed at, the bug curl fixed in 2018.

0
0
1
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1mo ago
ETW for Security Research: Providers, Sessions, and Detection Engineering https://idov31.github.io/posts/inside-etw-with-etwsuite
idov31.github.io

Ido Veltzman :: Security Research

0
0
1
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1mo ago
Mandatory User Profile for Persistence & EDR Evasion https://ipurple.team/2026/08/11/mandatory-user-profile/
Mandatory User Profile
Purple Team

Mandatory User Profile

The file NTUSER.MAN is a Windows user-profile registry hive used with mandatory profiles. It contains pre-defined configuration settings that are loaded into the registry (HKEY_CURRENT_USER) when t…

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Simple Job Board ≤ 2.11.0 - Unauthenticated RCE (CVE-2024-1813) https://mobeta.fr/simple-job-board-unauth-rce-cve-2024-1813/
mobeta.fr
0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Pollard's P-1 Factoring Algorithm in Plain C https://leetarxiv.substack.com/p/pollards-p-1-factoring-algorithm
Pollard's P-1 Factoring Algorithm in Plain C
leetarxiv.substack.com

Pollard's P-1 Factoring Algorithm in Plain C

Coding Pollard's 1974 Paper on Factoring Within P-1 Multiplicative Subgroups

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
CFP Open – Looking for Technical AI & Security Research for Après Slopes Summit 2027 https://www.aprescyber.com/
aprescyber.com
0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
The Risk of Fine-Tuned Open-Weight Models · MSec Operations Blog https://www.msecops.de/blog/posts/backdoored-llms/
msecops.de

The Risk of Fine-Tuned Open-Weight Models · MSec Operations Blog

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers https://blog.cloudflare.com/containers-cross-tenant-vulnerability/
How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers
Cloudflare Blog

How Cloudflare addressed a cross-tenant data exposure vulnerability in Containers

External security researchers at Accomplish identified a vulnerability in Cloudflare Containers that could expose residual disk data from previous workloads. We explain how the issue worked, how we investigated it, and the steps we took to remediate it.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Designing Patterns to Prevent IDOR https://sevhunt.com/docs/blog/designing-patterns-to-prevent-idor/
sevhunt.com

Designing Patterns to Prevent IDOR | SevHunt

0
0
1
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 1w ago
One Tap Too Far: Using Shortcuts to Bypass Chrome for iOS Call Prompts https://blog.doyensec.com/2026/09/24/chrome-ios-policy-bypass.html
blog.doyensec.com

One Tap Too Far: Using Shortcuts to Bypass Chrome for iOS Call Prompts · Doyensec's Blog

One Tap Too Far: Using Shortcuts to Bypass Chrome for iOS Call Prompts

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2w ago
Frame: Grounding LLM Vulnerability Detection with a Sound Separation-Logic Core https://lambdasec.github.io/Frame-Grounding-LLM-Vulnerability-Detection-with-a-Sound-Separation-Logic-Core/
Frame: Grounding LLM Vulnerability Detection with a Sound Separation-Logic Core — Lambda Security
Lambda Security

Frame: Grounding LLM Vulnerability Detection with a Sound Separation-Logic Core — Lambda Security

Frame is a neuro-symbolic SAST that pairs a sound separation-logic core with a verified, tiered LLM layer. On the Endor Labs real-world corpus it reaches 0.67 recall at 0.51 precision versus Semgrep

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Flying Eagle Android RAT: TLS Certificate Pivots, Panel Fingerprints, and 170 Servers Across Hong Kong ASNs https://hunt.io/blog/flying-eagle-android-rat-170-servers-night-dragon
hunt.io
0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Claude Mythos degrades HAWK and developed new exploit for round-reduced AES https://www.anthropic.com/research/discovering-cryptographic-weaknesses
anthropic.com

Discovering cryptographic weaknesses with Claude

Anthropic researchers find weaknesses in cryptographic algorithms with Claude Mythos Preview

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
What Every Programmer Should Know About Twists of Elliptic Curves https://leetarxiv.substack.com/p/twists-of-elliptic-curves
What Every Programmer Should Know About Twists of Elliptic Curves
leetarxiv.substack.com

What Every Programmer Should Know About Twists of Elliptic Curves

Twists Make Elliptic Curves Wildly Insecure. Here'a Cheatsheet Using Bitcoin's Familiar Secp

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
KindaRails2Shell: arbitrary file read to RCE in Rails Active Storage via libvips (CVE-2026-66066) https://ethiack.com/info-hub/research/kindarails2shell-rails-rce-cve-2026-66066
KindaRails2Shell - Critical RCE in Rails via Active Storage (CVE-2026-66066) | Ethiack
Ethiack

KindaRails2Shell - Critical RCE in Rails via Active Storage (CVE-2026-66066) | Ethiack

Ethiack research team discovered KindaRails2Shell (CVE-2026-66066): a critical RCE in Ruby on Rails via Active Storage. 500,000+ sites affected. Find out if you are and how to mitigate.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Code Execution via Provisioning Packages https://ipurple.team/2026/08/04/provisioning-packages/
Provisioning Packages
Purple Team

Provisioning Packages

Windows Provisioning Packages are used by Administrators to deploy configuration scripts on Windows environments by using a container format. Threat actors with elevated privileges could abuse prov…

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident https://huggingface.co/blog/agent-intrusion-technical-timeline
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident
huggingface.co

Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident

We’re on a journey to advance and democratize artificial intelligence through open source and open science.

0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
Sixteen strangers and a shared obfuscator: mapping the wool scene https://neurowinter.com/security/2026/07/28/the-cast-and-crew/
neurowinter.com
0
0
0
0
Open post
/r/netsec @_r_netsec@infosec.exchange
· 2mo ago
From wallet drains to a 12-year-old CryptoJS entropy bug: the Ill Bloom investigation https://www.coinspect.com/blog/ill-bloom-investigation/
Ill Bloom: Investigating a Wallet Generation Vulnerability During Active Exploitation
Coinspect Security

Ill Bloom: Investigating a Wallet Generation Vulnerability During Active Exploitation

How Coinspect traced a wallet-drain investigation back to a twelve-year-old insecure randomness flaw, searched for exposed addresses at scale, and disclosed the findings...

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 02:34:08 UTC