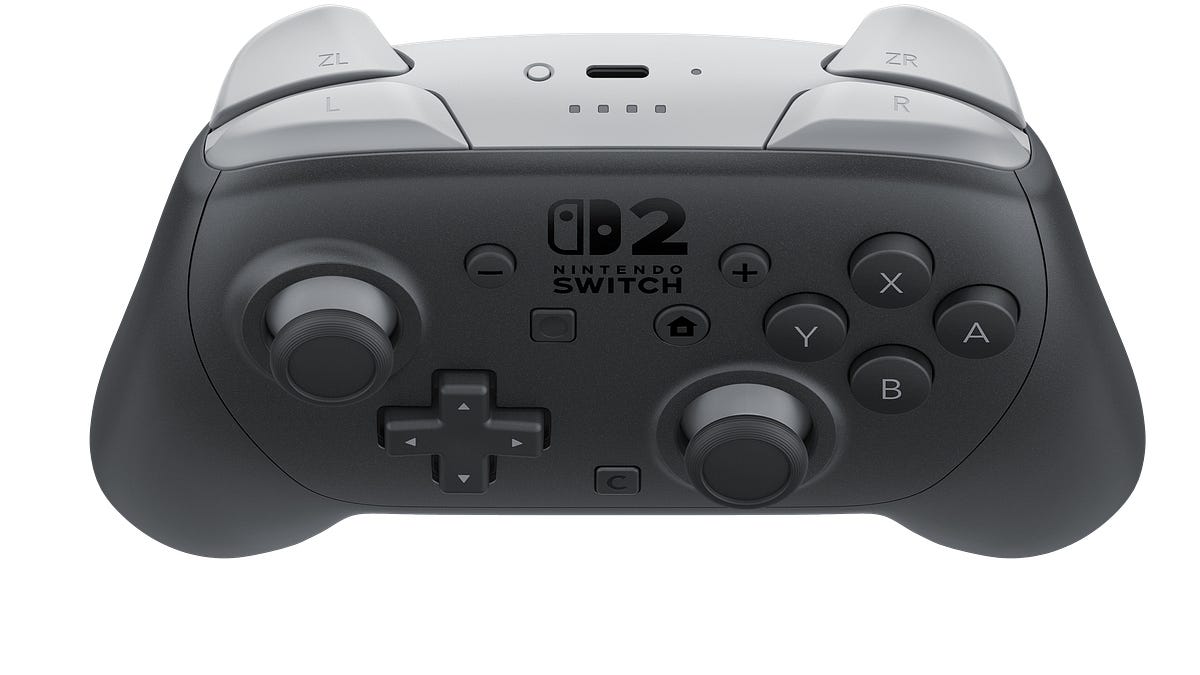
Two gamers have filed a class action lawsuit against Nintendo, alleging that the company will be unjustly enriching itself with any refund it secures from the U.S. government over widespread tariffs last year that, among other things, hiked the prices of Nintendo hardware and accessories.
“Unless restrained by this Court, Nintendo stands to recover the same tariff payments twice—once from consumers through higher prices and again from the federal government through tariff refunds, including interest paid by the government on those funds,” the suit states.
Remote
Open post
When you save passwords in Edge, the browser decrypts every credential at startup and keeps them resident in process memory. This happens even if you never visit a site that uses those credentials.
At the same time, Edge requires you to re‑authenticate before showing those same passwords in the Password Manager UI — yet the browser process already has them all in plaintext.
Edge is the only Chromium‑based browser I’ve tested that behaves this way. By contrast, Chrome uses a design that makes it far harder for attackers to extract saved passwords by simply reading process memory.
It decrypts credentials only when needed, instead of keeping all passwords in memory at all times. App‑Bound Encryption (ABE) adds another layer by binding decryption to an authenticated Chrome process, preventing other processes from reusing Chrome’s encryption keys.
Because of these controls, plaintext passwords appear only briefly during autofill or when the user views them, making broad memory scraping far less effective. The risk of keeping the passwords in cleartext in memory becomes evident in shared environments.
If an attacker gains administrative access on a terminal server, they can access the memory of all logged‑on user processes. In the video the attacker has compromised a user account with administrative rights and is able to view stored credentials for two other logged on
(or even disconnected) users with Edge running. I reported this to Microsoft, and the official response was that the behavior is “by design”. They have been informed that I would be sharing this as a responsible disclosure so users and organizations can make informed decisions
about how they manage credentials. Last wednesday (April 29th) I disclosed this on BigBiteOfTech by Norway
Simple, educational proof of concept, to show that the passwords are stored in cleartext in memory.
593
43
0
0
Open post
When you save passwords in Edge, the browser decrypts every credential at startup and keeps them resident in process memory. This happens even if you never visit a site that uses those credentials.
At the same time, Edge requires you to re‑authenticate before showing those same passwords in the Password Manager UI — yet the browser process already has them all in plaintext.
Edge is the only Chromium‑based browser I’ve tested that behaves this way. By contrast, Chrome uses a design that makes it far harder for attackers to extract saved passwords by simply reading process memory.
It decrypts credentials only when needed, instead of keeping all passwords in memory at all times. App‑Bound Encryption (ABE) adds another layer by binding decryption to an authenticated Chrome process, preventing other processes from reusing Chrome’s encryption keys.
Because of these controls, plaintext passwords appear only briefly during autofill or when the user views them, making broad memory scraping far less effective. The risk of keeping the passwords in cleartext in memory becomes evident in shared environments.
If an attacker gains administrative access on a terminal server, they can access the memory of all logged‑on user processes. In the video the attacker has compromised a user account with administrative rights and is able to view stored credentials for two other logged on
(or even disconnected) users with Edge running. I reported this to Microsoft, and the official response was that the behavior is “by design”. They have been informed that I would be sharing this as a responsible disclosure so users and organizations can make informed decisions
about how they manage credentials. Last wednesday (April 29th) I disclosed this on BigBiteOfTech by Norway
Simple, educational proof of concept, to show that the passwords are stored in cleartext in memory.
332
21
0
0