Remote
Dark Web Informer 
@DarkWebInformer@infosec.exchange
Website: https://darkwebinformer.com
Website Pricing (Crypto payments are fully automated): https://darkwebinformer.com/pricing
Socials: https://darkwebinformer.com/socials
API Access: https://darkwebinformer.com/api-details
About Dark Web Informer: https://darkwebinformer.com/about-dark-web-informer
X: https://x.com/DarkWebInformer
Updated: 2026-07-20
2318 Followers
2 Following
50 Posts
Joined April 11, 2024
Dark Web Informer:
X/Twitter:
🚨 Companies are being urged to shut down their NetScaler instances immediately due to multiple unpatched Citrix NetScaler RCE vulnerabilities.
Source: https://x.com/watchtowrcyber/status/2103891689857228803
Open post
🚨 🇵🇭 Initial access to the National Nutrition Council and LBC Express allegedly offered
⠀
The actor "realchimera" is advertising what they describe as full access involving two organizations in the Philippines:
• National Nutrition Council, a government organization
• LBC Express, a courier, cargo, and money remittance company
⠀
The listing claims the access includes government documents and user credentials. It does not identify the affected systems, number of accounts, access method, or price.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
2
0
0
0
Open post
🚨 🇫🇷 Planity customer and business data allegedly exposed
⠀
The actor "Syrv4x" has released a dataset they claim belongs to Planity, a French booking and management platform used by hair salons, beauty institutes, and barbershops.
⠀
The 12 MB file is advertised as containing 17,244 lines. Some of the claimed data includes:
• Customer names, email addresses, and phone numbers
• Business and customer identifiers
• Account usernames
• Appointment counts and booking frequency
• Revenue totals by service and product
• Deleted-account status
⠀
The sample contains a scraped_at timestamp dated September 22, 2026. The post does not explain how the information was obtained.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
2
0
0
0
Open post
‼️🇺🇸 An actor claims to be offering full GitHub organization access for Pfizer, including internal repositories, source code, and developer infrastructure.
3
0
1
0
Open post
🚨 Bitget reportedly suffered a hack resulting in more than $170 million in losses.
2
0
0
0
Open post
🚨 🇲🇽 GhostLeakers claims to have exposed phpMyAdmin credentials for ITESHU
⠀
The "GhostLeakers" team claims it obtained credentials for a phpMyAdmin instance belonging to Instituto Tecnológico Superior de Huichapan, a higher education institution in Hidalgo, Mexico.
⠀
The credentials are reportedly being distributed for free through the group’s Telegram channel. The post provides no evidence of successful access and does not claim that a dataset or institutional records were stolen.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
🚨 🇷🇴 Initial Access: Romanian Small Business Network
A threat actor is advertising administrative access to an unnamed Romanian business network reportedly generating approximately $1M in annual revenue.
The advertised access includes full admin control of a RouterOS gateway, three internal LANs, two WireGuard tunnels, WiFi credentials, and network reach across approximately 161 hosts.
The access is listed for around $150 in XMR.
This claim is currently unverified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
🚨 Forum actor offering 10% commission to brokers who find buyers for French and Belgian datasets
⠀
A forum actor using the handle "ChimeraZ" is recruiting intermediaries to help sell datasets associated with French and Belgian targets.
⠀
The actor says anyone who brings a buyer that purchases at least two datasets will receive 10% of the resulting revenue.
⠀
The advertised arrangement includes:
⠀
• Focus on French and Belgian datasets
• Minimum purchase of two datasets
• 10% commission on completed sales
• Example given: $100 commission on a $1,000 sale
• Contact handled through Session
⠀
The post suggests the actor is looking to expand distribution of previously advertised datasets by using third-party brokers to source buyers.
⠀
This activity is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
2
0
0
0
Open post
For the next hour you may see shoutbox alerts a little back to back, while I integrate the 30th forum.
1
1
0
0
Open post
I'm looking for some PAID OSINT tools. They need to accept crypto as payment. I'm working on some projects (people). Will share any information when it gets to that point.
Submit via: https://darkwebinformer.com/tips/
1
0
0
0
Open post
There is a bug on the Threat Feed where some forums are not showing any data when filtering by a specific forum. This should be fixed shortly.
1
1
0
0
Open post
‼️ Mikoyan Gurevich, a well-known OpSec and privacy advocate and Pitch moderator, has launched a Nitter Tor instance.
Onion: http://zcbxmgileoovnup5k4yj4w6r3vicqpawqc6b33rnmmsqy6n4micpzoad[.]onion/
2
0
1
0
Open post
‼️🇨🇦 Air Canada has been claimed a victim to The Gentlemen Ransomware
4
1
3
0
Open post
🚨 BREAKING: Chargeflow is notifying merchants of a security incident detected on September 20. The company says data from affected Shopify stores may have been involved.
⠀
Headquartered in New York, Chargeflow automates chargeback prevention and disputes for online merchants. GetLatka estimates its 2025 annual revenue at $16.4 million.
⠀
Potentially affected data includes customer contact details and addresses, order records, redacted payment details, payment metadata, and merchant profile information.
⠀
Chargeflow says full card numbers were not involved, Shopify logins and admin access were unaffected, and it has revoked and replaced the app access tokens. Its investigation is ongoing.
1
0
1
0
Open post
🚨 The U.S. Postal Inspection Service (USPIS) seized a major domain used to generate millions of fraudulent shipping labels, causing an estimated $126 million in losses for the U.S. Postal Service.
USPIS did not identify the domain or provide further information, and the link in its X post returns a 404 error.
1
0
0
0
Open post
🚨🇨🇱 DealerNET data and account access allegedly offered for 35 BTC
⠀
A forum actor using the handle "Karim000" claims to possess more than 100 GB of DealerNET data and access to over 5,000 platform accounts, including those used by banks, insurers, automotive businesses, and pension fund administrators.
⠀
Some of the claimed exposed material includes:
⠀
• Personal reports on Chilean citizens, journalists, and politicians
• Contact details and addresses
• Asset and vehicle information
• Family relationships and criminal records
⠀
The actor lists a price of 35 BTC and shares screenshots presented as samples.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
🚨🇫🇷 Autobacs customer and booking data allegedly leaked
⠀
A forum actor using the handle "0xDzz" claims to have released part of a dataset belonging to automotive parts retailer Autobacs, containing approximately 34,000 records totaling 159 MB.
⠀
Some of the claimed exposed material includes:
⠀
• Customer names, email addresses, and phone numbers
• Vehicle registration numbers
• Appointment dates and booking statuses
• Store identifiers
⠀
The displayed sample contains booking records dated 2021. The number of unique customers affected is not established.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
🚨🇫🇷 Mes Marchés dataset allegedly exposes 2,535 exhibitor records
⠀
A forum actor using the handle "Quantique" claims to have released a dataset from French platform Mes Marchés after accessing its API. The actor also claims to have scraped all hosted images.
⠀
Some of the claimed exposed material includes:
⠀
• Names, email addresses, and phone numbers
• Addresses and location coordinates
• Business identifiers and profile information
• Password, reset-token, and account verification fields
⠀
The post advertises a 1,000-record sample, with the full download gated behind eight forum points. The screenshot does not establish whether the password or token fields contain usable credentials.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
🚨🇫🇷 LVMH internal credentials and vulnerability information allegedly offered for sale
⠀
LVMH is a French luxury goods group spanning fashion, jewelry, cosmetics, wines, and spirits.
⠀
A forum actor using the handle "HollowCrimeCorp" claims to be offering a package of internal assets and information related to LVMH.
⠀
The advertised package includes:
⠀
• Internal URLs and access portals
• Administrator logins and passwords
• Confidential information and documents
• Alleged XSS, IDOR, and authentication bypass vulnerabilities
• Exposed API endpoints
⠀
The actor is inviting offers without listing a price. The post does not establish whether the credentials work or the claimed vulnerabilities have been exploited.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
🚨 Android spyware and RAT source code advertised for $500
⠀
A forum actor using the handle "greekdev" is advertising an Android surveillance application, including its client source code, server code, and web-based control panel.
⠀
Some of the claimed capabilities include:
⠀
• Live microphone, camera, and screen monitoring
• Call recording across messaging apps
• Keylogging, SMS tracking, and notification interception
• Access to files, contacts, and browsing history
• Remote device control and protection against removal
⠀
The actor promises updates for future Android versions, including Android 17, and requires payment through forum escrow.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
2
0
Open post
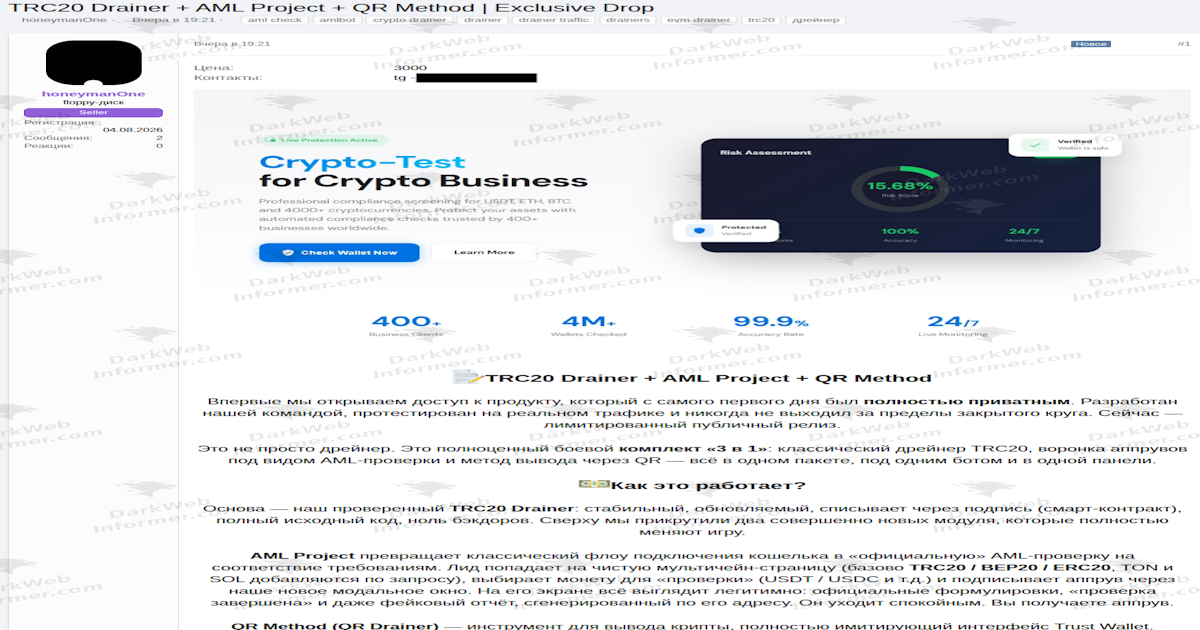
‼️ New Dark Web Informer Blog Post!
Title: TRC20 Drainer + AML Project + QR Method Offered as a 3-in-1 Crypto Theft Kit
Link: https://darkwebinformer.com/trc20-drainer-aml-project-qr-method-offered-as-a-3-in-1-crypto-theft-kit/
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
1
0
0
0
Open post
🚨🇫🇷 L'Orange Bleue data allegedly exposing 732K+ subscribers and 440K+ IBANs offered for sale
⠀
L'Orange Bleue is a French fitness and gym network.
⠀
A forum actor using the handle "Venus1337" claims to be selling data associated with L'Orange Bleue after allegedly gaining access to an administrative panel and identifying an IDOR vulnerability affecting an export function.
⠀
Key details:
• 732,385 subscribers allegedly affected
• 440,326 IBANs claimed
• Profile pictures reportedly included
• Actor claims the export endpoint requires no authentication
• No rate limiting is allegedly in place
⠀
Claimed exposed data includes:
• Full names
• Dates of birth
• Addresses
• Phone numbers
• Email addresses
• IBAN and BIC information
• Membership and subscription details
• Profile pictures
⠀
The actor claims the vulnerable export functionality can be accessed without credentials and says requests can be sent at a high rate, potentially allowing large-scale extraction of customer records.
⠀
The breach claim, subscriber and IBAN counts, vulnerability details, and full scope of the exposed dataset have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
‼️ New Ransomware Group: n0n
http://nongzecboljwv3yfndkggsybsglfrkffw7bvk2zemuteoxe6etpusnad[.]onion
1
0
1
0
Open post
🚨🇺🇸 U.S. auto insurance dataset containing 683K+ records allegedly leaked
A forum actor using the handle ElMagoSpeak, with a collaborator identified as Z3r00, claims to have released a dataset containing 683,387 records associated with U.S. automobile insurance customers.
Claimed exposed data includes:
⠀
• Full names
• Paternal and maternal surnames
• Street addresses
• Cities and states
• Postal codes
• Telephone numbers
• Vehicle class
• Vehicle make
• Vehicle body type
• Vehicle identification numbers (VINs)
• Gender
• Income information
The source of the records, affected insurance provider or providers, authenticity of the dataset, stated record count, and full scope of the exposed information have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
1
0
Open post
‼️🇫🇷 LunarisSec claims a vulnerability in the site paris-ouest[.]fr. 👇
https://x.com/DarkWebInformer/status/2100306626947285329
1
0
0
0
Open post
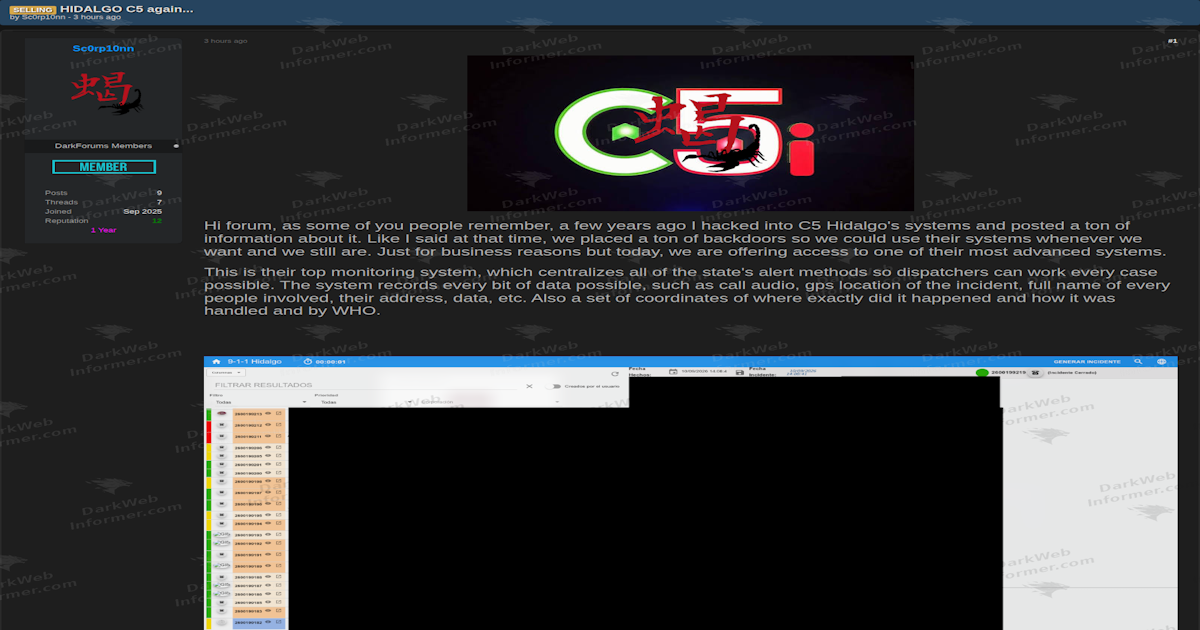
‼️ New Dark Web Informer Blog Post!
Title: Hidalgo C5 Emergency Dispatch System Access Allegedly Offered for Sale
Link: https://darkwebinformer.com/hidalgo-c5-emergency-dispatch-system-access-allegedly-offered-for-sale/
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
1
0
0
0
Open post
🚨🇲🇽 Mexican patient dataset containing 100K medical records allegedly leaked
⠀
The affected healthcare organization is not identified in the listing. The post only describes the material as Mexican patient and medical data.
⠀
A forum actor using the handle xexa claims to have leaked a dataset containing information tied to approximately 100,000 patients in Mexico.
⠀
Claimed exposed data includes:
⠀
• Patient names
• Home addresses
• Identification numbers
• Medical identification numbers
• Patient-related medical records
• Personally identifiable information
• Other healthcare-related data
⠀
The actor states the dataset is approximately 5 MB uncompressed and is distributing the purported records through a forum download.
⠀
The source of the data, affected healthcare organization, record count, and authenticity of the dataset have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
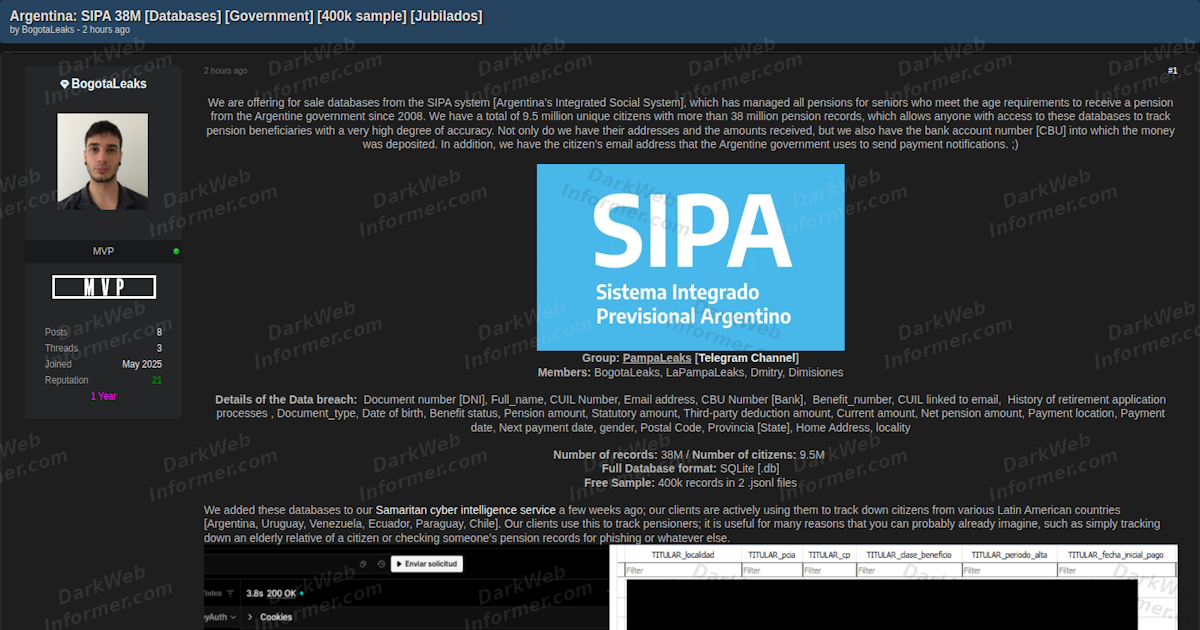
‼️ New Dark Web Informer Blog Post!
Title: Argentina SIPA Pension Dataset Claim Covers 38M Records and 9.5M Citizens
Link: https://darkwebinformer.com/argentina-sipa-pension-dataset-claim-covers-38m-records-and-9-5m-citizens/
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
1
0
0
0
Open post
🚨🇺🇸🇵🇰 F-16 engine-related technical documents allegedly leaked online
⠀
The F-16 Fighting Falcon is a multirole combat aircraft originally developed in the United States and operated by numerous countries, including Pakistan.
⠀
A forum actor using the handle mosad claims to have released documents described as F-16 engine design material, publishing multiple photographed pages as purported samples.
⠀
The samples appear to include:
⠀
• Engine system schematics
• Component diagrams
• Technical illustrations
• Maintenance or servicing procedures
• Fuel and control-system diagrams
• Engine-related reference material
⠀
The actor is distributing the purported archive for free and has published download information alongside the samples.
⠀
The origin, classification status, authenticity, and connection of the documents to U.S. or Pakistani F-16 operations have not been independently verified. The samples alone are also insufficient to confirm that the material constitutes actual engine design documentation.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
1
0
0
0
Open post
‼️ New Ransomware Group: Владивосток or Vladivostok in English
Dark Web: http://dr5beljvyqljgq5ppro57pgetg4yeslcsexmuhvv3p46wod3odsh3fid[.]onion
The message in the second screenshot says:
"Welcome to the blog of the new "Vladivostok" group of companies! We are open for business; our contact details will be published shortly. We are ready to collaborate with researchers, penetration testers, and disgruntled employees. Our partners will receive a generous share—negotiated to potentially reach up to 60% of the total value."
0
0
0
0
Open post
🚨 Sasai Fintech source code allegedly stolen and released
⠀
The actor "888" claims responsibility for a September 2026 breach of Sasai Fintech, a pan-African digital financial services and technology company.
⠀
The actor claims to have stolen and released the company’s source code. A file tree is provided as a sample, but the affected applications and volume of code were not disclosed.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0
Open post
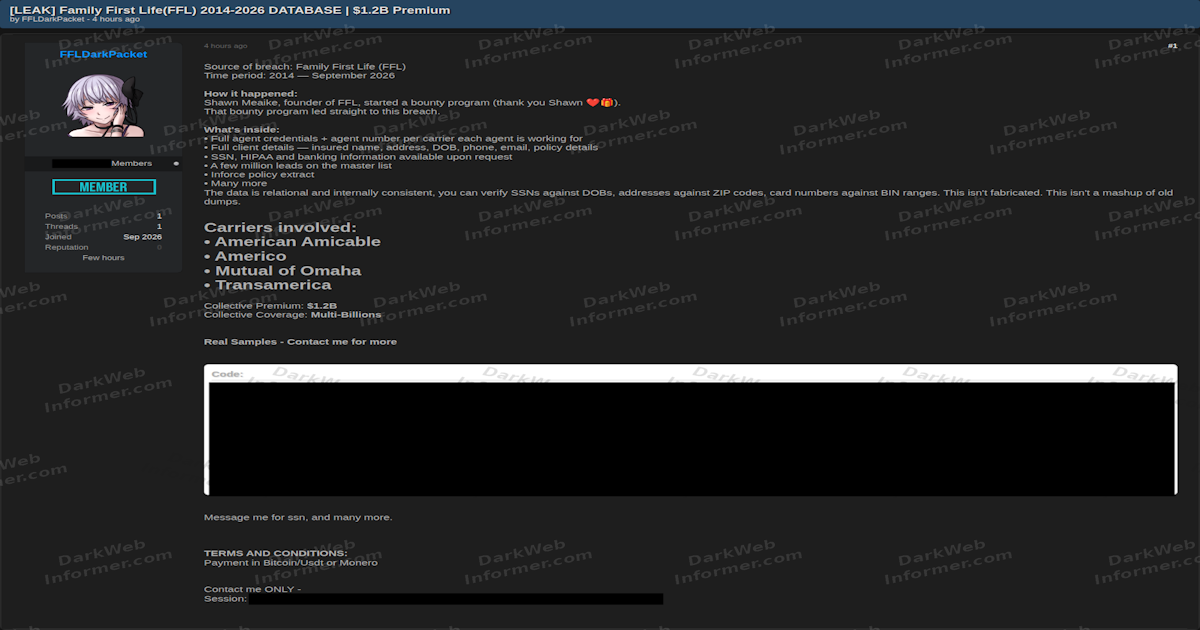
‼️ New Dark Web Informer Blog Post!
Title: Family First Life Dataset Claim Includes Agent Credentials, Client PII and Banking Data
Link: https://darkwebinformer.com/family-first-life-dataset-claim-includes-agent-credentials-client-pii-and-banking-data/
💥 Get early visibility into underground claims, including unblurred screenshots, before they turn into headlines: https://darkwebinformer.com/pricing
0
0
0
0
Open post
🚨 Actor seeks crypto trading intelligence from logs, account access, and API keys
⠀
A forum actor using the handle "Theriella" is seeking partners who can provide cryptocurrency trading intelligence derived from logs, compromised access, or API keys.
⠀
The actor claims to have capital available for decentralized exchange trading, mentioning an initial $5,000 test and up to $10,000 for testing, with a proposed 50% profit share.
⠀
The recruitment post seeks:
⠀
• Insider information: actionable trading intelligence linked to access involving victims or large cryptocurrency holders
• API keys: exchange API access without trading permissions to study large holders’ activity
• Supporting evidence: proof of access, relevant addresses, and prior results
• Ongoing partnerships: sources of information who lack capital to act on it themselves
⠀
The actor claims a previous partner supplied intelligence through numerous trading-terminal API keys. They exclude trading bots, referral schemes, paid signals, and exchange or peer-to-peer arbitrage.
⠀
The post does not identify affected platforms or establish that any accounts have been compromised or profitable trades completed.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0
Open post
🚨🇫🇷 Hôpital Paris Saint-Joseph dataset allegedly exposing 15K+ records
Hôpital Paris Saint-Joseph is a nonprofit private hospital in Paris providing care across multiple medical specialties.
⠀
A forum actor using the handle "weykofa" claims to have obtained and released data associated with Hôpital Paris Saint-Joseph, advertising 15,061 individual records and information tied to 738 doctors.
⠀
Claimed exposed data includes:
⠀
• Names and internal identifiers
• Email addresses
• Doctor-related records
• Account/status fields
• Record creation and update timestamps
⠀
The actor says the material consists of three CSV files totaling approximately 1.3 MB and published sample records as purported proof.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0
Open post
‼️🇺🇸 Emperador Ransomware claims a U.S. Woman's health care provider
🇺🇸 Alabama Woman's Health Care - A Huntsville, Alabama healthcare provider offering consultative medicine, wellness, and aesthetic care services.
The listing claims 2.5 GB of data, including several thousand employee and client documents and an archive of photographs.
0
0
0
0
Open post
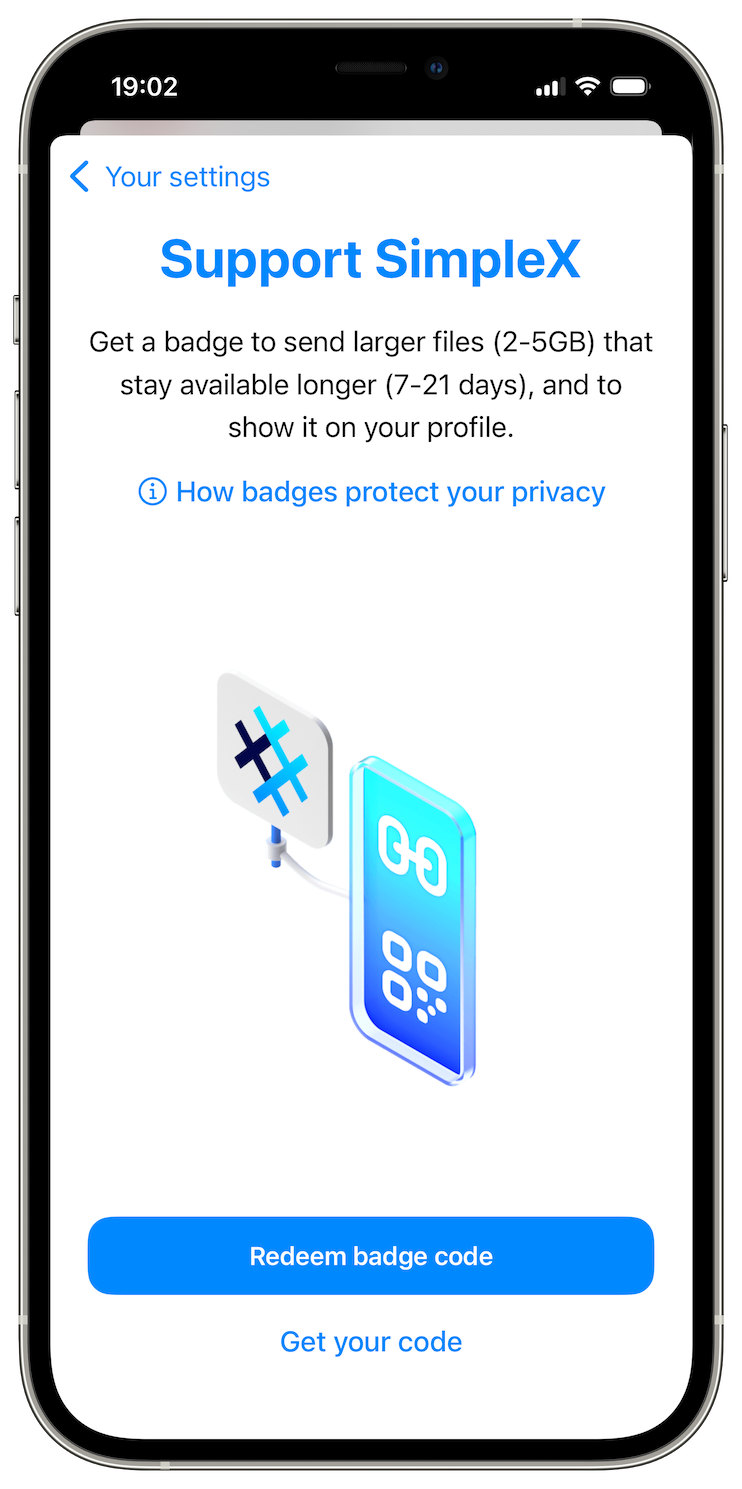
🔐 SimpleX Chat launches privacy-preserving supporter badges with larger file limits
SimpleX Chat has introduced supporter badges in the v7.1 beta, giving users additional features without tying the purchase to a persistent account or identity.
⠀
Supporter badge perks include:
• Files up to 2 GB instead of 1 GB
• File storage extended to 7 days
• Badge displayed on your SimpleX profile
⠀
A higher "Legend" badge increases file limits to 5 GB and keeps files available for up to 21 days.
⠀
The privacy-focused part is how the badge works.
The credential is stored locally on the user's device and is never directly sent to contacts or servers.
Instead, SimpleX generates a new zero-knowledge proof whenever the badge needs to be verified, revealing only the badge type and expiration date.
SimpleX says the proofs cannot be linked to each other or back to the original purchase.
⠀
Badges can currently be purchased by card, Bitcoin, or Monero (nice) and redeemed inside the app without creating an account or enabling automatic renewal.
Future plans include using the same system for longer backup retention and higher server rate limits.
Source: https://simplex.chat/blog/20260919-simplex-supporter-badges.html
0
0
0
0
Open post
🚨 Malware developer advertises cross-platform RAT and crypter for $500
⠀
A forum actor using the handle "Consecration" is advertising what they claim is a newly developed all-in-one command-and-control platform supporting Windows, Linux, and Android systems alongside a built-in crypter.
⠀
Key details:
• Windows, Linux, and Android support
• Integrated RAT/C2 platform and crypter
• $500 asking price
• XMR preferred
• Lifetime access advertised
• Limited to 10 buyers
• Self-hosted deployment available separately
⠀
Claimed capabilities:
The Windows component is advertised with remote shell access, file transfers, process injection, credential harvesting, keylogging, screen and microphone capture, token manipulation, lateral movement, persistence, proxying, and multiple defense-evasion features.
⠀
The Android component reportedly includes SMS, contacts, call logs, location, camera, microphone, clipboard and account collection, remote shell access, screen recording, remote control, persistence, and anti-analysis functionality.
⠀
The Linux component is advertised with shell execution, file transfers, credential collection, keylogging, persistence, lateral movement, network discovery, proxying, and data exfiltration capabilities.
⠀
The included crypter is claimed to support multiple encryption and obfuscation methods, anti-debugging, anti-sandbox and anti-VM checks, delayed execution, junk-code injection, rotating build keys, and other techniques intended to complicate analysis.
⠀
The actor says demonstrations are available before purchase and that transactions can be completed through a verified forum middleman.
⠀
This claim and the advertised capabilities have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
1
0
Open post
🚨 🇧🇪 Judo Vlaanderen dataset with 98,000 member records and plaintext passwords offered for sale
⠀
The actor "RedStone" is selling a dataset they claim belongs to Judo Vlaanderen, the Belgian judo federation serving Flanders.
⠀
The listing advertises 1.8 million rows across 99 tables. Some of the claimed data includes:
• 98,495 member records with names, dates of birth, addresses, emails, phone numbers, and nationalities
• More than 75,000 plaintext password entries
• 1,248 cleartext Okta credentials
• 539 national identification numbers
• 271 clubs, including 250 IBANs and 159 company numbers
• Email, payment, event registration, and competition records
⠀
A sample containing 1,000 records was shared with the listing. The post does not explain how the data was obtained.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0
Open post
👀ShinyHunters provided an updated message to Cl0p Ransomware.
"UPDATE, 20 Sep, 1:39 a.m ET: Dear Likhogray & Tarasov, tell your boss j0nny to wake the fuck up. Run those pockets. I want all the money you made off the EBS campaign plus more AND WITH INTEREST. before I start releasing information regarding the companies that paid you, how much, and to what Bitcoin address. My phone book contains all major financial media outlets. CLOCK IS TICKING! LETS GET THE BALL ROLLING! Be sure to bring an English interlocutor so you can comprehend my literacy in acquiring your bank account. 66 hours remaining."
0
0
0
0
Open post
🚨 Roundcube SQL injection flaw actively exploited months after patches were released
The Canadian Centre for Cyber Security has warned that CVE-2026-48842, a high-severity vulnerability in Roundcube Webmail, is being exploited in the wild.
⠀
Roundcube is an open-source webmail application that lets people access email through a browser.
The flaw affects its virtuser_query plugin and allows SQL injection before authentication.
⠀
Key details:
• CVSS score: 8.1
• No attacker credentials required
• No user interaction required
• Affects Roundcube 1.6.x before 1.6.16 and 1.7.x before 1.7.1
⠀
Roundcube released the original fixes on May 24, 2026. Canada added the exploitation warning to its advisory on September 21, citing open-source reporting.
The advisory does not identify the attackers, victims or scale of exploitation.
⠀
Administrators should update affected installations promptly. Newer security releases, 1.6.19 and 1.7.4, also address additional vulnerabilities.
Source: https://www.cyber.gc.ca/en/alerts-advisories/roundcube-security-advisory-av26-503
0
0
0
0
Open post
🚨 ShinyHunters resumes mass exploitation of critical Oracle PeopleSoft flaw using simple WAF bypass.
Mandiant and Google Threat Intelligence Group have identified renewed mass exploitation of CVE-2026-35273 by UNC6240, also known as ShinyHunters.
⠀
The critical vulnerability allows unauthenticated remote code execution in Oracle PeopleSoft PeopleTools and carries a CVSS score of 9.8.
Oracle released an emergency patch on June 10.
⠀
The new campaign targets organizations that attempted to mitigate the flaw using web application firewall rules but did not install the patch.
ShinyHunters bypassed rules blocking the vulnerable /PSEMHUB/ endpoint by encoding a single character and sending requests to /%50SEMHUB/.
⠀
Google says web shells were deployed on dozens of systems worldwide across:
• Higher education
• Technology
• IT services
• Healthcare
• Agriculture
• Transportation
• Government
⠀
The actors deployed web shells, the SIDEEYE backdoor, Neo-reGeorg tunneling tools and MeshAgent for persistent remote access.
Around one-quarter of the observed commands executed with root or SYSTEM privileges.
⠀
Organizations running PeopleSoft should patch immediately, disable or remove the Environment Management Hub where possible and investigate encoded variants of /PSEMHUB/ in access logs.
WAF rules alone are not sufficient.
0
0
0
0
Open post
🚨🇨🇳 Momo dataset allegedly exposing 154M+ records offered for sale
⠀
Momo is a Chinese social networking and dating platform that allows people to connect, chat, and discover others nearby.
⠀
A forum actor using the handle "666op" claims to be selling a dataset associated with Momo containing more than 154 million unique records. The collection is dated September 2026 and is advertised for $800.
⠀
Claimed exposed data includes:
⠀
• Identity data: nicknames, real names, gender, birth dates, age
• Contact/location data: phone numbers, province and city
• Account data: registration dates, last activity, status and verification flags
• Device data: operating system and installation channel
• Profile data: membership, wealth/charm levels and constellation
• Social data: followers, following, moments and gift activity
• Platform data: Momo coins, host status and account levels
⠀
The actor published sample records containing profile, account, device and demographic information as purported proof of the dataset.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0
Open post
‼️🇺🇸 n0n Ransomware claims United Federation of Teachers
🇺🇸 United Federation of Teachers (UFT) - A New York City labor union representing teachers and other education professionals.
The listing claims approximately 181,420 legal case documents could be published, including grievance and arbitration files, disciplinary appeals, personnel case files, collective bargaining agreements, MOUs, health-benefit case materials, teacher evaluations, class-size complaints, and staff search and case-view audit logs.
0
0
0
0
Open post
‼️🇺🇸🇮🇷 Wallstreet names two victims
🇺🇸 Odyssey Charter School, Inc. - A U.S.-based nonprofit organization operating tuition-free public charter schools.
🇮🇷 Roshd Sanat - An Iranian industrial company providing engineering, manufacturing, and related industrial services.
0
0
0
0
Open post
🚨🇵🇦 Panama Ministry of Economy and Finance dataset allegedly leaked
Panama’s Ministry of Economy and Finance is the government agency responsible for national economic policy, public finances, budgeting, taxation, and fiscal administration.
A forum actor using the handle TerroahOver claims to have compromised the ministry and leaked information associated with individuals in its systems.
Claimed exposed data includes:
⠀
• Full names
• Surnames
• Social Security numbers
• Cédula / national identity numbers
⠀
The actor published sample records as purported proof of the leak and attached additional material to the post.
The breach claim, source of the data, number of affected individuals, authenticity of the sample, and full scope of the exposed dataset have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0
Open post
‼️🇺🇸 Another forum post for CenterPoint Energy
🚨🇺🇸 CenterPoint Energy breach actor publishes full context on alleged 6.7M-customer data theft
⠀
CenterPoint Energy is a major U.S. electric and natural gas utility serving customers across several states, including Texas and Minnesota.
⠀
A forum actor using the handle Hex_4d722e4d656f77 has published additional details about the previously claimed CenterPoint Energy breach, alleging that approximately 6,734,894 customer records totaling around 48.8 GiB were extracted on August 21, 2026.
⠀
Claimed exposed data includes:
⠀
• Customer names
• Phone numbers
• Email addresses
• Service and billing addresses
• Account and premise identifiers
• Billing amounts and past-due balances
• Billing and due dates
• Service and rate information
• AutoPay and paperless billing status
• Driver’s license numbers
• Last four digits of Social Security numbers
⠀
The actor claims the data was obtained by enumerating customer account numbers through improperly protected guest-facing API functionality, with additional identity information exposed through a second account-verification function.
⠀
According to the post, the extraction was split across seven parallel data ranges covering Texas and Minnesota. The actor also claims that later security changes, including CAPTCHA enforcement, eventually stopped further collection.
⠀
The actor has now published what they describe as the full CenterPoint Energy dataset for download.
⠀
The breach claims, record count, technical explanation, and authenticity of the released dataset have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
1
Open post
👀 🚨 VMware vCenter exploit advertised for $55,000
⠀
VMware vCenter is used to centrally manage virtual machines and ESXi hosts.
⠀
An actor using the handle "Lalo" is selling a claimed one-day exploit that can reset a vCenter administrator account’s password. The seller claims no public exploit code is available.
⠀
Advertised capabilities include:
⠀
• Python-based vulnerability checking and exploitation
• Administrator account takeover with network access
• Instructions for resetting ESXi root passwords after compromise
⠀
The asking price is $55,000 plus escrow fees. No CVE identifier or affected versions are provided.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
0
0
0
0