Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Black Lantern Security (BLSOPS)

@BlackLanternLLC@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

By analyzing and simulating the most relevant attacks, Black Lantern Security delivers solutions that provide immediate reductions in organizational risk.

23 Followers
6 Following
22 Posts
Joined November 30, 2022
Discord:
https://discord.gg/7mAHbSJDB
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 2mo ago
IBM webMethods Integration Server CVE-2026-12118. Developed, found, and reported by research from BLSOPS. #CVE #vulnerability #cybersecurity #IBM https://open.substack.com/pub/blacklanternsecurity/p/cve-2026-12118-ibm-webmethods-integration?r=rbmdk&utm_campaign=post&utm_medium=web&showWelcomeOnShare=true
open.substack.com
1
1
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 6mo ago

Our AI chatbot passed every prompt injection test we threw at it. Then we just asked it nicely for customer data, and it happily obliged.

New from our ASMOC team, how a vibe-coded website with LLM became a high-risk finding on a client's attack surface.

https://blog.blacklanternsecurity.com/p/artificial-foolishness-the-hidden

Artificial Foolishness: The Hidden Dangers of External-Facing LLMs
blog.blacklanternsecurity.com

Artificial Foolishness: The Hidden Dangers of External-Facing LLMs

The rise of AI opens more doors to attackers

1
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 7mo ago

It's time for the next question of our OSINT insight quest!

Q2: What is the single biggest missing feature you would like to see in BBOT?

Thx for sharing!

1
0
1
1
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 7mo ago

Over the next few weeks we're hoping to gain some insight from the novice & veteran users of subdomain enumeration / OSINT tools via polls.

Q1: What's your favorite OSINT tool?

If your favorite isn't listed, post feedback in the comments.

Thx for participating!

1
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 8mo ago

🚨CVE-2026-2103: Infor Syteline ERP hard-codes encryption keys in binaries. One copy = universal decryption of ALL passwords, DB creds & API keys across every install. No patch.
#CVE
https://blog.blacklanternsecurity.com/p/cve-2026-2103-infor-syteline-erp

CVE-2026-2103 - Infor Syteline ERP
blog.blacklanternsecurity.com

CVE-2026-2103 - Infor Syteline ERP

Infor Syteline ERP

1
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 8mo ago

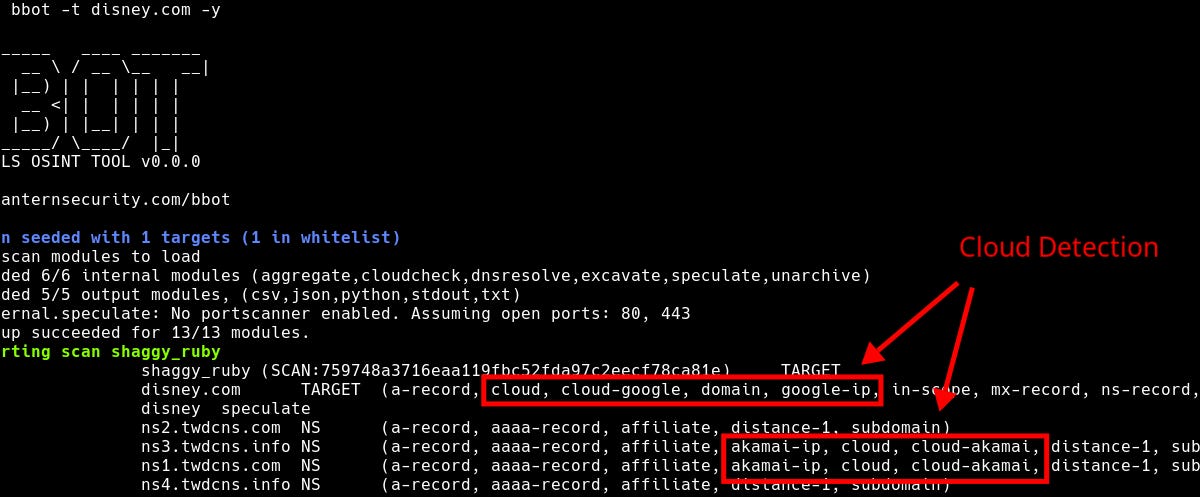
👀 Recon friends, stop guessing your target’s infra.
CloudCheck is LIVE — 56+ providers, daily-updated sigs, Rust/Python/CLI & a FREE REST API.
BBOT now fingerprints cloud / CDN / WAF in milliseconds.
https://blog.blacklanternsecurity.com/p/introducing-cloudcheck-comprehensive
#OSINT #BugBounty #Infosec #ASM

Introducing CloudCheck: Comprehensive Cloud Provider Detection
blog.blacklanternsecurity.com

Introducing CloudCheck: Comprehensive Cloud Provider Detection

An overhaul of BBOT's cloud detection

1
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 11mo ago

📢New drop in our #ASM series! Shadow IT, rogue subdomains, leaked creds—your attack surface is exploding! Discover the 3 goals for Attack Surface Management: 24/7 discovery, risk-based triage, measurable fixes. Read now 👇 https://blog.blacklanternsecurity.com/p/attack-surface-management-asm-goals #Infosec

Attack Surface Management (ASM): Goals, Objectives, and Business Case
blog.blacklanternsecurity.com

Attack Surface Management (ASM): Goals, Objectives, and Business Case

“I shouldn’t be able to even reach that from here”

1
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 16mo ago

🚨 ALERT! 🚨 Over 260,000 #Joomla sites at risk due to TWO newly discovered #zeroday vulnerabilities! 😱 Learn how our team uncovered these critical flaws in a popular Joomla extension and how you can protect yourself. Read the full story: https://blog.blacklanternsecurity.com/p/doomla-zero-days #cybersecurity #websecurity #CVE

Doomla! Zero Days
blog.blacklanternsecurity.com

Doomla! Zero Days

Discovery and Exploitation of two Zero Days from the perspective of a first year Penetration Tester.

1
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 4mo ago

🚨CVE-2026-10880: OSNEXUS QuantaStor up to v6.6.1 has an unauthenticated blind SQL injection in the login form. No credentials required. Attackers can recover stored password hashes one character at a time using differing login error responses.
https://blog.blacklanternsecurity.com/p/cve-2026-10880-osnexus-quantastor

blog.blacklanternsecurity.com

CVE-2026-10880 - Osnexus Quantastor 9.8 Unauthenticated SQL Injection

Osnexus Quantastor 9.8 Unauthenticated SQL Injection

0
0
2
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 4mo ago

📢 Now hiring: Senior Software Engineer - Python Developer (Remote)

We're looking for someone with deep Python async experience, Rust chops, & a real open-source track record to build security tooling.

Details & apply → https://www.blacklanternsecurity.com/careers/

blacklanternsecurity.com

Black Lantern Security - Cybersecurity Services Company

Black Lantern Security - Cybersecurity Services Company

0
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 6mo ago

🚀red-run 2.0 is live. Key updates:
Claude Code agent teams: each agent in its own tmux pane; hit Esc to pause or redirect in real time
New state-mgr teammate tracks findings and keeps the attack graph current
Still a lean, lab-focused CTF solver.

https://open.substack.com/pub/blacklanternsecurity/p/red-run-20-agent-teams?r=rbmdk&utm_campaign=post&utm_medium=web&showWelcomeOnShare=true
open.substack.com
0
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 6mo ago

We've made it to the last question of the month!

We'd like to know: Have you used BBOT's web modules such as spider or lightfuzz? Give us some feedback on those modules if you have.

Swag give-away next week!

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 6mo ago

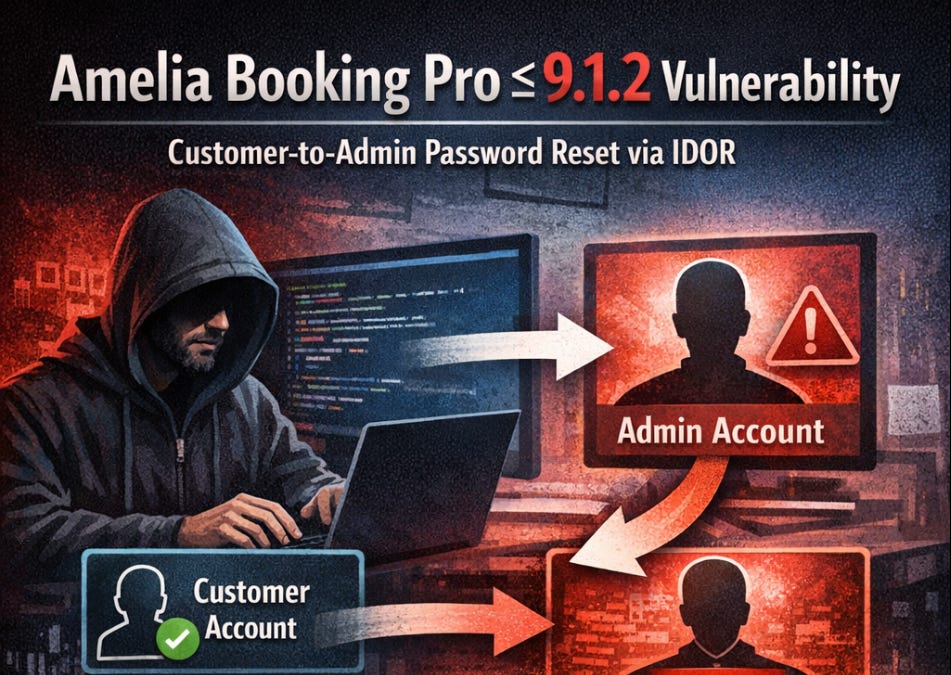
From customer to admin takeover in one request—Amelia Booking Pro flaw enables full WordPress compromise. #CVE-2026-2931 is on the BLS Blog now!
https://blog.blacklanternsecurity.com/p/amelia-booking-pro-912-authenticated

Amelia Booking Pro ≤ 9.1.2: Authenticated Customer-to-Admin Password Reset via IDOR
blog.blacklanternsecurity.com

Amelia Booking Pro ≤ 9.1.2: Authenticated Customer-to-Admin Password Reset via IDOR

CVE-2026-2931

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 6mo ago

This week, we want to know: Were there any obstacles during your first experience with BBOT? If so, what were they?
We also want to share some swag with this month. We'll enter survey participants (one entry per question) into a drawing for a chance at some sweet BLS merch💜.

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 7mo ago

New post on the BLS Blog! Red Run walks through designing a compact native .NET loader that starts fast & keeps a low profile. The write-up covers inner workings & build steps.
Dive in: https://blog.blacklanternsecurity.com/p/red-run?r=qkvb8&utm_campaign=post&utm_medium=web&triedRedirect=true

red-run
blog.blacklanternsecurity.com

red-run

All work and no tokens makes Claude a dull boy...

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 8mo ago

Manspider 2.0 Release
New features include:
1) Better text extraction with Kreuzberg
2) Unit tests for stability
3) uv + ruff
4) Filtering on file modification time (thanks to https://github.com/probird5)
Install with: uv tool install man-spider
https://github.com/blacklanternsecurity/manspider

GitHub

probird5 - Overview

probird5 has 27 repositories available. Follow their code on GitHub.

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 8mo ago

We’ve rolled out BBOT 2.8, packed with major updates since 2.3New module: gitdumper by @Domwhewell
New module: lightfuzz by @paulmmueller(replaces dastardly)
New module: medusa by @ChristianFl (for SNMP brute forcing)
New module: github_usersearch by @Domwhewell
New module: aspnet_bin_exposure by @paulmmueller
New module: graphql_introspection by @mukesh-dream11
New module: retire.js by @paulmmueller
New module: legba by @ChristianFl and @fuzikowski (for brute-forcing tons of services)
Countless improvements + fixes

Release history: https://www.blacklanternsecurity.com/bbot/Stable/release_history/
#BBOT #opensource #cybersecurity

blacklanternsecurity.com

Release History - BBOT Docs

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 8mo ago

🚨 TREVORspray 2.4 drops w/ TENANT ENUM!
Big thanks to Sprocket Security for uncovering the secret API — details: https://sprocketsecurity.com/blog/tenant-enumeration-is-back
Update to the latest version with pipx upgrade trevorspray
Spray smarter, not harder. #RedTeam #InfoSec

sprocketsecurity.com
0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 11mo ago

🚨 CVE-2025-12463: an unauth’d SQL injection that, when skillfully weaponized, can leak or overwrite critical data.
PoC + full teardown + hardening tips are live.
Full details👇https://blog.blacklanternsecurity.com/p/cve-2025-12463-98-unauthenticated

#infosec #CVE #SQLi

CVE-2025-12463— 9.8 Unauthenticated SQL Injection in Guetebruck G-Cam Series Cameras
blog.blacklanternsecurity.com

CVE-2025-12463— 9.8 Unauthenticated SQL Injection in Guetebruck G-Cam Series Cameras

Smile, you’re on camera.

0
0
1
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 13mo ago

🚨Still on TecCom TecConnect 4.1? Blind XXE (CVE-2025-10183) in OpenMessaging lets unauth attackers:
• exfil any file (PoC: win.ini) via OOB
• snag & relay NTLM hashes
• own the box with one SOAP request
Upgrade to Connect 5. Full details➡️BLS Blog👇https://blog.blacklanternsecurity.com/p/teccom-tecconnect-41-xml-external?r=1cn8gh

blog.blacklanternsecurity.com
0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 17mo ago

🎉 BBOT just hit 1 MILLION downloads in 3 years!

From a small idea to a powerful recursive OSINT tool, this journey was only possible because of YOU — the users, contributors, & community who shared, tested, & believed. 💜🖤

Thank you🙏. We’re just getting started.

0
0
0
0
Open post
Black Lantern Security (BLSOPS) @BlackLanternLLC@infosec.exchange
· 3mo ago
A new Linux kernel-level exploit (@florian@infosec.exchange Roth), An AI-Hallucinated espionage claim (@jessica@infosec.exchange Lyons) Hundreds of domains associated with Netnut seized (@KrebsOnSecurity_rss@burn.capital) And more! All in this weeks CrowsNest post. posthttps://crowsnest.blacklanternsecurity.com/posts/crows-nest-2026-07-06/
crowsnest.blacklanternsecurity.com
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 06:55:28 UTC